On November 19, 2025, INNOCOM received its third ISO/IEC 27001 certification, this time under the ISO/IEC 27001:2022 standard, further demonstrating its capabilities in information security management. This significant milestone reflects the company’s ongoing efforts to strengthen information security standards, protect customer data, and develop secure, reliable technology solutions.
INNOCOM Achieves ISO/IEC 27001 Certification for the Third Time
On November 19, 2025, INNOCOM Business Consulting and Technology Co., Ltd. was once again certified for its Information Security Management System under the international ISO/IEC 27001:2022 standard by SIS Certifications.
Previously, INNOCOM had received ISO/IEC 27001:2013 certification twice, marking important progress in establishing and standardizing its information security management system in accordance with international standards.
Obtaining ISO 27001 certification for the third time, now under ISO/IEC 27001:2022, further demonstrates INNOCOM’s commitment to information security management and its efforts to continuously improve its management system to meet the growing demands of the technology and digital transformation sectors.
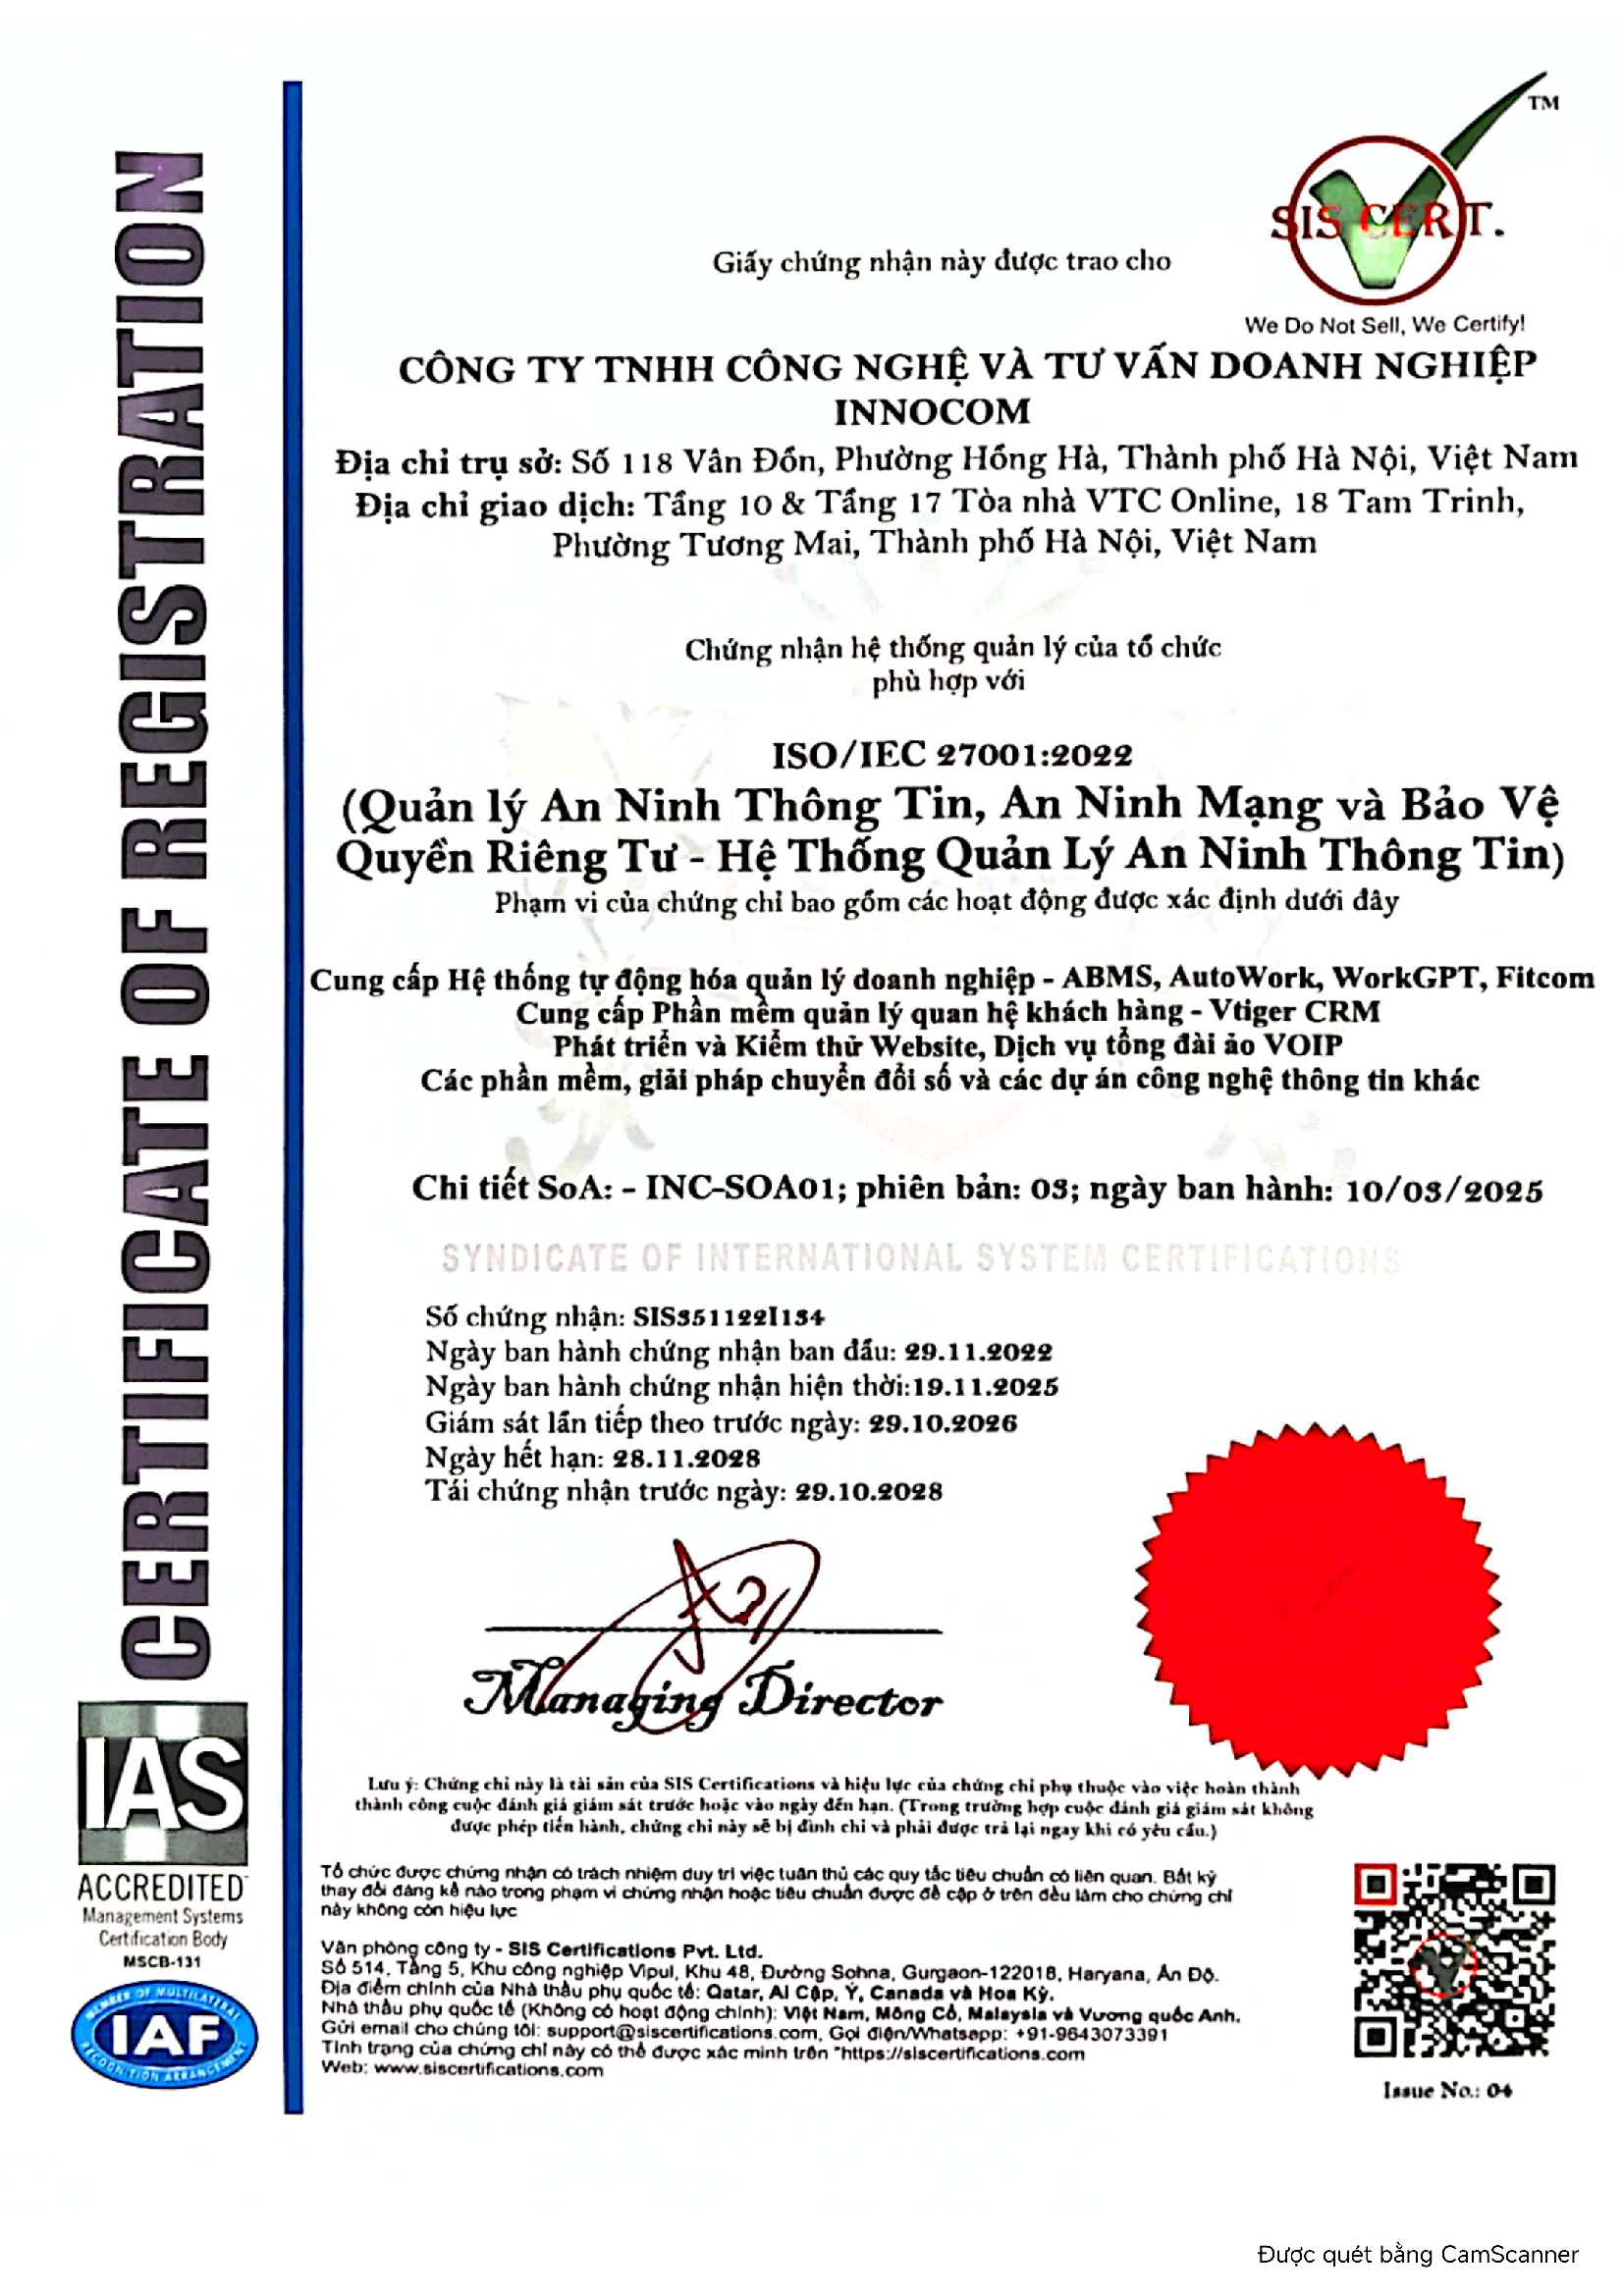
ISO/IEC 27001:2022 Information Security Management System Certification
ISO/IEC 27001:2022 Certification – An International Standard for Information Security
What Is ISO/IEC 27001:2022?
ISO/IEC 27001:2022 is an international standard for Information Security Management Systems (ISMS). It specifies requirements for organizations to establish, operate, maintain, and continually improve their information security management systems.
The standard focuses on three core principles: confidentiality, integrity, and availability of information. These principles help businesses proactively identify risks, control access rights, and protect data against information security threats.
The ISO/IEC 27001:2022 edition was published in October 2022, replacing ISO/IEC 27001:2013 with updates better suited to modern technology environments, particularly cybersecurity, cloud computing, and data protection.
Which Organizations Issue ISO/IEC 27001:2022 Certification?
The ISO/IEC 27001:2022 standard was developed and published by two international standardization organizations:
ISO (International Organization for Standardization): An international organization that develops and publishes standards.
IEC (International Electrotechnical Commission): An international organization that develops standards for electrical, electronic, and related technologies.
ISO and IEC publish standards but do not directly certify businesses. Assessments and certifications are carried out by independent certification bodies with the appropriate expertise.
For INNOCOM, ISO/IEC 27001:2022 certification was issued by SIS Certifications on November 19, 2025, confirming that the company’s information security management system meets the requirements of the standard within the certified scope.
What Requirements Must Businesses Meet to Obtain ISO/IEC 27001:2022 Certification?
To obtain ISO/IEC 27001:2022 certification, businesses must establish and operate an information security management system that meets the standard’s requirements and undergo an assessment by an independent certification body.
Key requirements include:
Establishing an information security management system: Defining the scope, security policies, objectives, and management responsibilities.
Assessing and treating risks: Identifying threats related to data, systems, and business operations, and developing appropriate controls.
Controlling access and protecting data: Implementing access permissions, account management, information protection, and safeguards against unauthorized access.
Providing security awareness training: Improving employees’ awareness of and responsibility for information protection.
Monitoring and continually improving: Conducting internal audits, management reviews, corrective actions, and ongoing improvements to management effectiveness.
Businesses must demonstrate that their processes and security controls are implemented in practice, rather than existing only as documentation or written policies.
How Widely Recognized Is ISO/IEC 27001:2022 Certification?
ISO/IEC 27001 is one of the most widely recognized international standards for information security management, adopted across many countries and industries, including technology, finance, manufacturing, and services.
According to the ISO Survey 2022, more than 70,000 ISO/IEC 27001 certificates were recorded across 150 countries, illustrating the standard’s widespread adoption and applicability worldwide.
For businesses, ISO/IEC 27001 certification offers several benefits:
Enhancing credibility and building trust with customers and partners.
Demonstrating the ability to manage risks and protect information in line with international standards.
Improving professionalism in technology system management and operations.
Creating a competitive advantage when working with organizations that have stringent information security requirements.
Read more: INNOCOM Awarded ISO 27001:2013 Information Security Certification
Demonstrating INNOCOM’s Information Security Capabilities Across Its Technology Solutions
As a company operating in technology and digital transformation, INNOCOM places strong emphasis on building an information security management system to protect data throughout the development, implementation, and operation of solutions for customers.
Within the scope of its ISO/IEC 27001:2022 certification, INNOCOM’s activities include:
Providing business management automation systems, including ABMS, AutoWork, WorkGPT, and Fitcom.
Providing Vtiger CRM customer relationship management software.
Developing and testing websites and providing virtual VoIP telephony services.
Providing other software products, digital transformation solutions, and information technology services.
In the technology and digital transformation sector, INNOCOM’s third ISO/IEC 27001 certification represents an important milestone that helps strengthen customer and partner confidence in its technology solutions, including ABMS, WorkGPT, Vtiger CRM, and other digital transformation services.
INNOCOM Reaffirms Its Commitment to Supporting Secure Digital Transformation
As digital transformation continues to accelerate, information security has become a key factor in ensuring business stability and sustainable growth.
From ISO/IEC 27001:2013 to ISO/IEC 27001:2022, INNOCOM’s third ISO/IEC 27001 certification reaffirms its commitment to developing technology with information security at its core. Moving forward, INNOCOM will continue to improve its management system, enhance service quality, and support businesses in achieving secure, efficient, and sustainable digital transformation.
INNOCOM will continue to improve its management system, enhance product and service quality, and strengthen security measures to deliver secure, efficient, and sustainable digital transformation solutions to Vietnamese businesses.
Contact INNOCOM today at 1900.068.895 to explore our diverse ecosystem of secure digital technology solutions!